Processor SecOps helps protect technology environments
Processor SecOps brings together modular managed security solutions focused on prevention, detection, response and compliance — from automated vulnerability remediation to continuous monitoring, active threat protection and intelligent orchestration across cloud and endpoints.Get to know the many possibilities offered by Processor SecOps:


Professional Services for cybersecurity
Processor’s Professional Services for Security brings together all the technological know-how we have acquired to strengthen organizations’ cybersecurity culture through technical consulting and security assessments, protection-solution projects and implementation, specialized support and incident response, identity and access management, and security education and training.


SecOps Care for 365
SecOps Care Processor is Processor's recurring specialized support service for Microsoft 365 cybersecurity capabilities, combining technical assistance, operational support, and the guided application of best practices to sustain critical environments, strengthen regulatory compliance, and drive continuous security evolution with operational predictability and governance.
Monitoring and Observability
With LiveWatch Monitoring, monitor your operations in real time, 24x7, with artificial intelligence that detects anomalies before they become problems. Reduce failures, improve performance, and gain full visibility into your infrastructure, applications, and devices with customized dashboards and data-driven support.


Asset inventory
With LiveWatch Discover, continuously and automatically map your IT assets, with intelligence that identifies risks, waste and optimization opportunities.Optimize costs, improve governance and gain strategic visibility into infrastructure, applications and services, with an up-to-date inventory, intelligent alerts and integration with FinOps, security and compliance processes.


LiveWatch Security Hub
The LiveWatch Security Hub is Processor’s offering for organizations that need continuous security visibility, structured event detection and guided response.
Workstation and server protection
With SecOps Patch Manager, automate patch management across servers and endpoints — Windows, macOS, Linux, and third-party apps — with a SharedOps model that combines efficiency, compliance, and security. Reduce risk, optimize updates, and maintain full control with clear, actionable reports.


Advanced ransomware protection
SecOps xDR provides advanced ransomware protection with intelligent detection and automated endpoint response. Using Machine Learning, AI and the SharedOps model, the solution combines online/offline protection, virtual patching and coordinated remediation to keep your operation secure and available.

Directory Manager by Processor
Directory Manager by Processor is the solution for centralized control of digital identities in complex, distributed environments. It combines technology, automation and continuous auditing, and can be used directly by the customer or operated by Processor under a BPO model, with specialized teams taking on critical routines and promoting ongoing governance.


Alignment with CIS Benchmark security controls
Continuous or point-in-time compliance assessment service against CIS benchmarks, including security configuration checks for operating systems, applications, cloud services and devices, with remediation recommendations and automation, delivered in FullOps format.
risk assessment
Business risk assessment, prioritization of remediation efforts and creation of a plan for security demands.
data protection
Solutions to minimize the attack surface against cyberattacks and preserve data integrity, as well as backups and disaster recovery plans.
monitoring
24/7 security and monitoring, log retention for auditing, internal security events with global assessments of external threat levels.
vulnerability scanning
Identification of security gaps and weaknesses in internally and externally published services, with periodic alerts.
incident detection and response
Immediate response to security events, crisis management, assessment of environments under active and preventive attack, and definition of remediation actions.
Risk and vulnerability analysis
Business risk assessment, prioritization of remediation efforts, and creation and adjustment of the SecOps plan
Security architecture
Development of the security architecture and policies, definition of SecOps modules, and selection of the technologies to be used
Implementation and adjustment of security policies
Deployment of planned SecOps modules, technologies and security policies
Monitoring, incident response and support
Activation and management of monitoring, threat response and incident response solutions to support contracted security environments
Awareness and Verification
Promoting practices that encourage accountability and attention to cybersecurity. Checking user effectiveness and best practices
Process Control and Performance Management
Environment assessment and continuous improvement, service-level measurement, incident management and an overview of ongoing activities according to the contracted SecOps modules
risk analysis
Business risk assessment, prioritization of remediation and creation of a plan for security demands
security architecture plan
Technical discussions bringing together technical and business knowledge on security policy planning and objectives
implementation of the new security policies
Implementation of security technologies and policies according to the organizational architecture and defined objectives
operations and consumption
Support and operation of deployed security environments, allowing customer teams to focus on evolving environments and optimizing them
process control
Routine checks of the security environment, its policies and observations for continuous improvement
performance management
Through LiveCloud, the customer controls contracts and consumption and manages billing for each environment down to the resource level
Security as a service in an integrated format, through our SecOps Journey
Zero Trust + Processor’s specialization with Microsoft in IAM and CCoE
Zero Trust is not an isolated solution — it is a strategic model for continuous security operations. It is based on three non-negotiable principles: explicitly validate every access request, apply the principle of least privilege, and assume that breaches can occur.

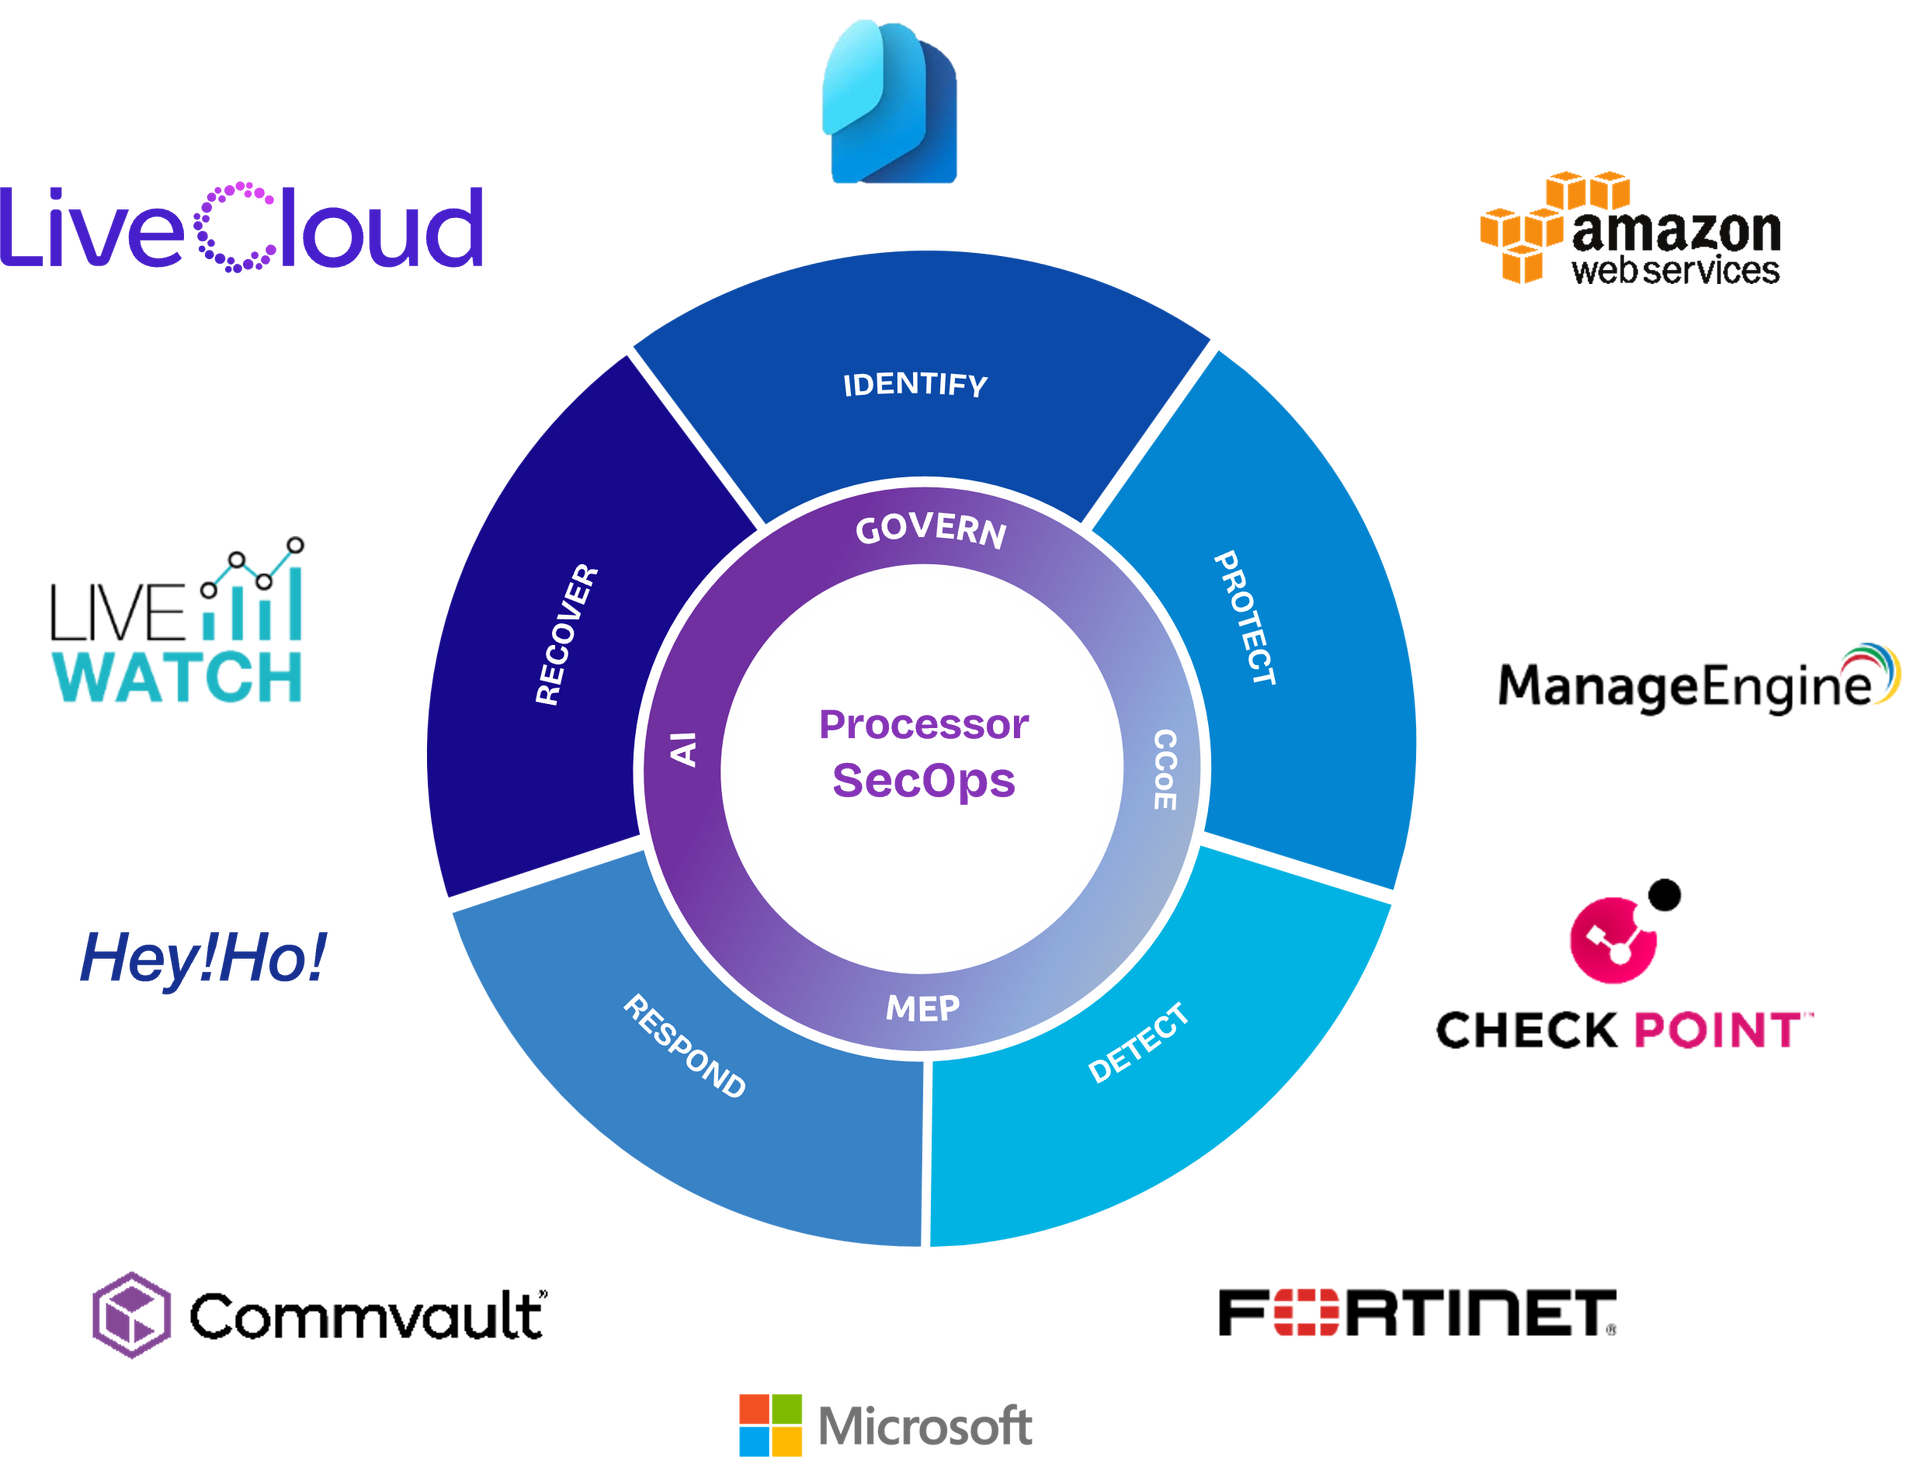
Key technologies used in Processor SecOps

Benefits for our customers
Strategic alignment and mapping
Fosters alignment between security and business objectives, maps the operating environment and develops a secure architecture.
Resilience and operational continuity
Strengthens protection against supply chain threats, promotes post-incident operational continuity and conducts periodic testing.
Security culture and awareness
Promotes a security culture, conducts forensic incident investigations and manages access to protect against threats.
Proactive threat and risk management
Provides insight into and proactive action against cyber risk by identifying, assessing and mitigating vulnerabilities.
Operational efficiency and governance
Improves the effectiveness of security controls, ensures oversight and compliance, and conducts tests to identify vulnerabilities.
Proactive detection and rapid response
Implements solutions for proactive prevention and detection, identifies suspicious activity early and responds quickly to incidents.
Security insights
Data protection is one of the most critical challenges facing companies and individuals today. The increasing sophistication and frequency of cyberattacks underscore the importance of implementing measures to protect against data loss, criminal interception and misuse.
With this in mind, we created some content to help broaden your perspective on the topic. Check it out:
Want to learn more?
Fill out the form and our team of experts will contact you: