


SecOps xDRAdvanced protection against ransomware
Automated, real-time endpoint protection
A comprehensive security solution specifically designed to protect organizations’ servers and workstations, on-premises or in the public cloud, with state-of-the-art technology using behavioral analysis.
Security as a Service
Detection of new and existing threats, with incident response based on Machine Learning and Artificial Intelligence for highly critical environments.
Orchestrated incident response
Predictable operating costs
EDR & XDR
Protection for workstations, servers, factory systems and IoT
Threat prevention and intelligence
Threat Hunting & Threat Intelligence Advanced forensic analysis, MITRE ATT&CK-based hunting, and management of indicators of compromise (IOCs).
Anti-Ransomware & Anti-Bot ProtectionBehavioral detection mechanisms, protection against exploits and malware, and communication with botnets.
Cloud Threat Feeds: Integration with global intelligence databases for agile response to emerging threats.
EDR (Endpoint Detection and Response)
Telemetry collection, behavioral analysis and coordinated real-time incident response.
Sandboxing and CDR (Content Disarm & Reconstruction) Isolation and secure reconstruction of suspicious files to prevent malicious payloads from executing.
Browser Security Native protection during browsing, preventing web-based exploitation.
Zero-Day Phishing Protection
Prevention against phishing attacks, even on newly created pages, without relying on signatures.
GenAI Security Data leakage control in generative AI tools.
DLP (Data Loss Prevention) Advanced rules for protecting against information loss and leakage
Posture Management Monitoring and adjustment of endpoint security configurations, reducing exposure and non-compliance.
Access Control & Remote Access VPNApplication control, local firewall, device compliance and integrated VPN for secure remote connections.
Full Disk Encryption Disk encryption and removable media protection to prevent physical data leakage.
With SecOps xDR, the organization gets
Advanced protection with Machine Learning and Artificial Intelligence
Predefined scan schedules
Dashboard via a management platform with environment management information
Ability to create playbooks for automated remediation
Solution management focused on continuous availability and prevention
Proactive advanced security solution
Complete visibility, including installed software and processes
Up to two environment reports per month, on demand
Protection at every stage of the attack
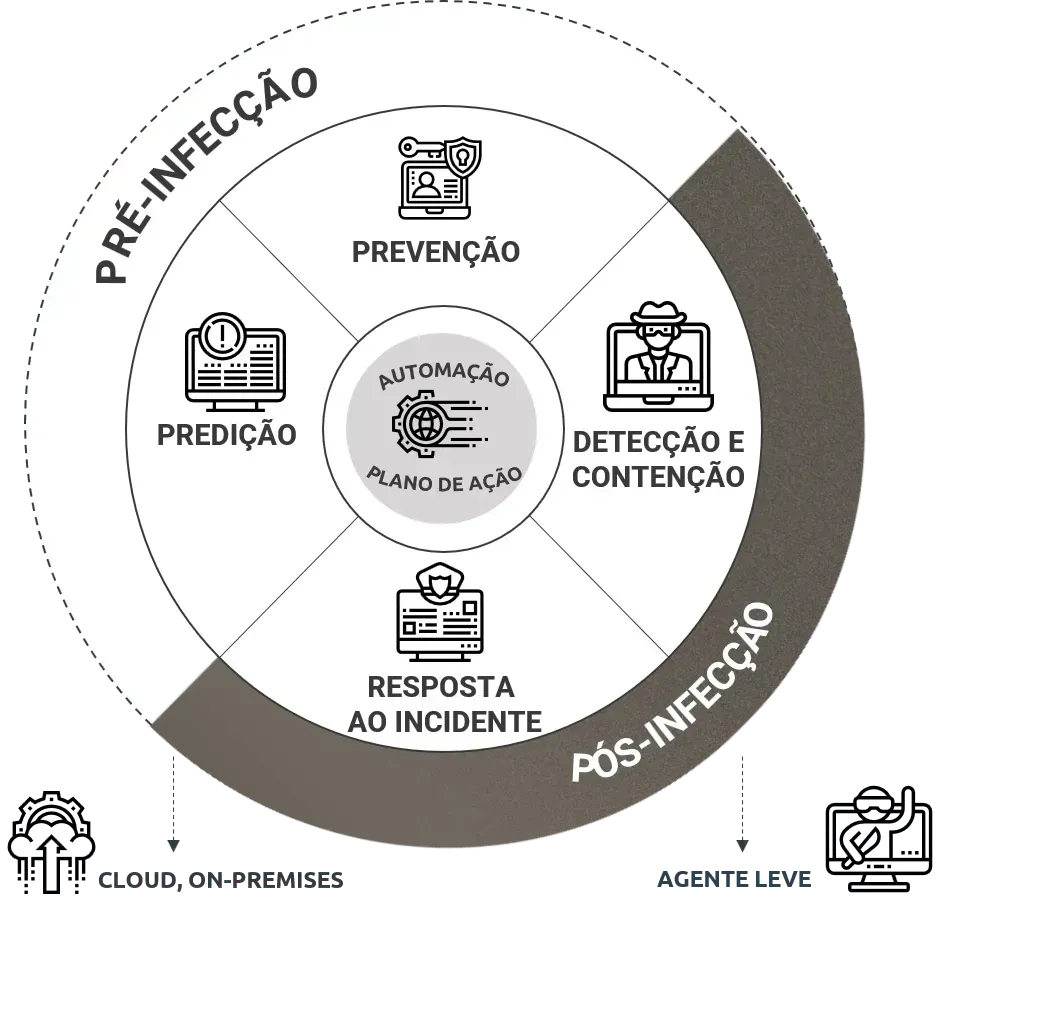
PRE-INFECTION
Discovery
Prediction
POST-INFECTION
Detection
Neutralization
Response and Investigation
Remediation and Rollback
SecOps Care for xDR
Specialized support for incident detection and response
The SecOps Care for XDR is Processor’s complementary service for organizations that need specialized support for XDR detection and response capabilities. The solution supports alert analysis, incident response and threat containment, with structured technical guidance, defined SLAs and governance,
What the service adds to the solution
- Specialized support for analyzing security alerts and events
- Technical guidance for incident response and containment
- Executive threat dashboards and reports
- 8x5 support, with an option for ad hoc 24x7 support for critical incidents
- Critical support-initiation SLA of up to 1 hour, according to criticality
When does it make sense to add SecOps Care Patch Manager?
- Security incidents requiring a fast, specialized response
- Environments without a dedicated SOC or with limited response capacity
- Scenarios requiring structured guidance to contain damage
- Need for technical support during critical events
SecOps Care for XDR provides specialized technical guidance for rapid decisions and effective incident containment, reducing uncertainty at critical moments and supporting response with method, clarity and governance.

Benefits for our customers

- Proactive, real-time, automated protection with orchestrated incident response across all supported platforms.
- With a cloud-native infrastructure and a small footprint, SecOps xDR can be deployed quickly and scaled to protect hundreds of thousands of endpoints.
- It can support a variety of enterprise use cases. Endpoints are protected both online and offline.
- Investment optimization and predictability per device.
- SecOps xDR offers a single console and is managed by our Managed Services team, providing your company with management information for financial oversight of your contracts, ticket creation and visibility across all contracted services.


LiveCloud Detection & Response
Want to learn more?
Fill out the form and our team of experts will contact you:


